Two-Factor Authentication (2FA)
Platform, Security & Integrations / Security
Two-Factor Authentication (2FA)
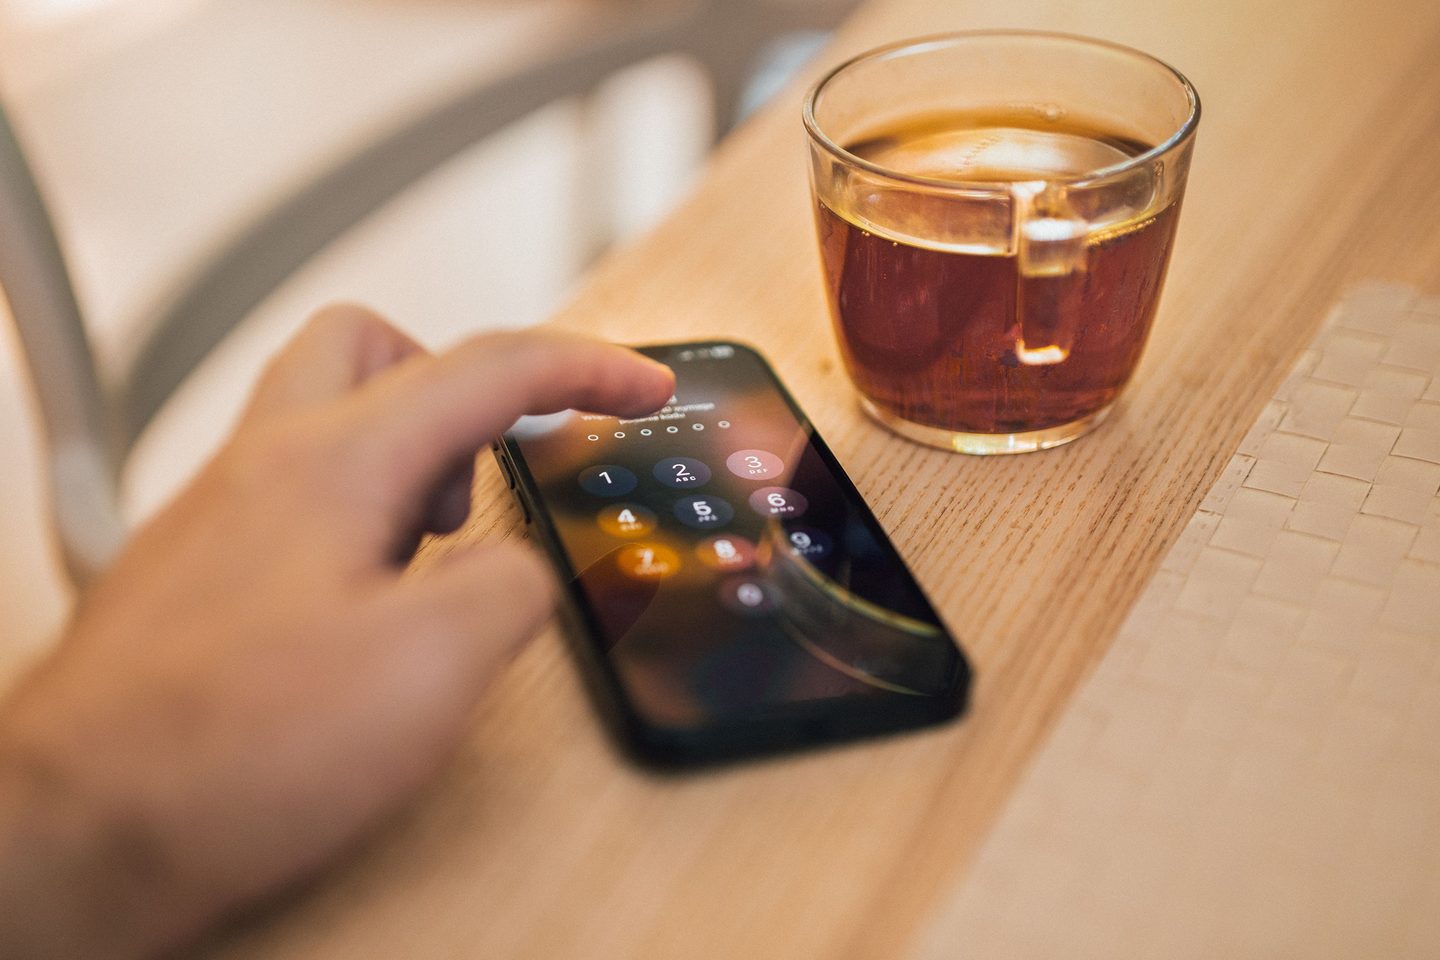
Two-Factor Authentication (2FA — see Glossary) requires a second proof of identity — typically a one-time code from an authenticator app or email — in addition to a password, so a stolen or guessed password alone isn’t enough for someone to log in.
Why does this matter for a phone system specifically?
Passwords leak — through phishing, reused credentials, or data breaches on other sites that have nothing to do with your business. 2FA means that even if someone compromises a password, an attacker still can’t get into the admin portal or an employee’s account without also having access to their phone or email for that one-time code.
Where does 2FA apply — just the admin portal?
You can apply it across the admin portal, the softphone and mobile apps, and any connected management tools, not just the main administrator login. Which logins require it is configurable based on your business’s risk tolerance.
Do employees have to use it every single time they log in?
Not necessarily — you can configure trusted-device exemptions so a recognized device doesn’t need to re-verify every time. This strikes a balance between security and day-to-day convenience, while still requiring the second step from a new or unrecognized device.
What if we already use 2FA through Microsoft or another identity provider?
If your business already enforces 2FA through Single Sign-On with a provider like Microsoft Azure AD, that protection carries over automatically — there’s no need to configure a separate, duplicate 2FA system on top.
Do we require 2FA, or is it optional?
You can turn it on, and we strongly recommend it, particularly for administrator accounts, but your business’s own security policy decides which accounts require it.